DURAI RTO DR4K0N

Offensive security specialist and penetration tester. I find vulnerabilities before the bad actors do. Certified professional with proven CTF competition wins.

TECHNICAL ARSENAL

Network & Web Exploitation

  • Burp Suite
  • Nmap
  • Wireshark
  • Metasploit

Fuzzing & Cracking

  • Ffuf
  • Hydra
  • Hashcat

Identity & Access Management

  • BloodHound
  • Active Directory
  • Entra ID

Cloud & Azure Recon

  • Azure CLI
  • ROADtools
  • AADInternals

Infrastructure

  • Linux
  • Networking

Other Skills

  • Blender

CERTIFICATIONS & AWARDS

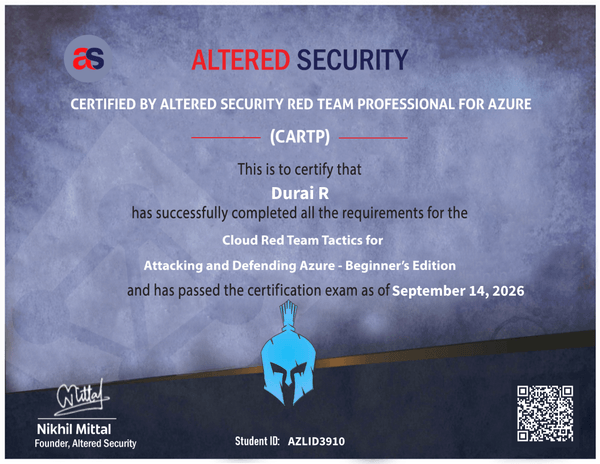
Certified Azure Red Team Professional
Altered Security / 2025 - Active

CARTP

Certified Azure Red Team Professional

Certified API Security Analyst
APIsec University / 2025 - Active

CASA

Certified API Security Analyst

APIsec Certified Practitioner
APIsec University / 2025 - Active

ACP

APIsec Certified Practitioner

FIELD RECONNAISSANCE & ONGOING LABS
CCEPCertified Cyber Exploitation ProfessionalRedTeamLeader
AD RED TEAMEnterprise Active Directory & Cloud Red TeamingHands-on Adversary Simulation

THE OPERATOR

I'm a cybersecurity enthusiast and aspiring security engineer with hands-on experience in penetration testing, vulnerability assessment, and security research. Passionate about offensive security, I actively explore web, network, and cloud security concepts while building practical projects and participating in Capture The Flag (CTF) competitions.

I enjoy learning about emerging threats, ethical hacking methodologies, and secure system design. Beyond technical skills, I'm committed to continuous learning, responsible disclosure, and contributing to the cybersecurity community through research, writeups, and collaborative projects.

Currently focused on strengthening my knowledge in cloud security, Active Directory security, container security, and AI/ML security fundamentals.